Cybersecurity Week in Review: September 28 – October 4, 2026
Cyberattacks, data breaches, zero-days, and global responses. Discover the biggest cybersecurity headlines of this week.
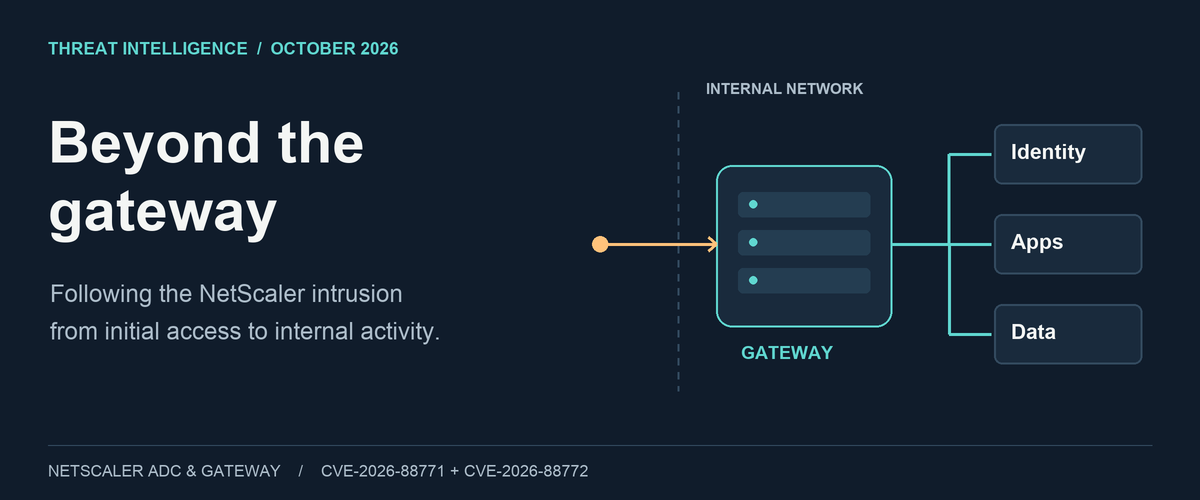
NetScaler: Following the Intrusion Beyond the Gateway
Two exploited zero-days, a foothold on the gateway, and a response that must reach into the internal network. A CTI and SOC reading of the September NetScaler disclosures.
Cybersecurity Week in Review: September 21–27, 2026
Cyberattacks, data breaches, zero-days, and global responses. Discover the biggest cybersecurity headlines of this week.